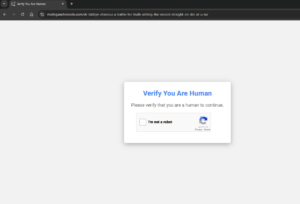
















Meme coin listing and token display pages are becoming new phishing hubs, with attackers exploiting token metadata to redirect crypto traders to fake Cloudflare verification screens.
Hackers update community token information with malicious website links, which are automatically displayed on decentralized tracking platforms. At least one victim reportedly lost $600,000 in the attacks.
im a fucking dumb retard and it just cost me $600k
i actually hate my fucking life
— danny (@cladzsol) September 15, 2026
The scam uses a technique known as ClickFix. When users click the fake “Verify you are human” checkbox, JavaScript secretly copies a malicious command to their clipboard. The page then instructs victims to open PowerShell or Terminal, paste the command, and press Enter to complete the verification. Executing the script can install information-stealing malware, such as Lumma Stealer, which searches for sensitive files, browser data, and crypto wallet credentials.
Crypto traders should never paste commands into Terminal or PowerShell to resolve website verification issues. Legitimate services such as Cloudflare do not require users to execute administrative scripts for CAPTCHA verification. Traders should close suspicious token pages immediately and consider keeping their primary crypto wallets separate from browsers used to explore unfamiliar meme coins.
Crypto users share ClickFix warnings after Danny’s loss
Following Danny’s reported loss, security commentators and crypto users highlighted how fake Cloudflare verification pages exploit familiarity and user distraction. Sam Security explained that legitimate Cloudflare checks do not require users to open PowerShell, noting that ClickFix attacks rely on victims manually entering malicious commands, allowing the activity to bypass conventional download-based detection.
a real cloudflare check never asks you to open powershell. that’s the whole attack, it’s called clickfix. nothing downloads, you type it yourself, so nothing gets scanned.
— Sam Security (@samseclabs) September 16, 2026
Another user shared an experience involving a juice-selling website that displayed a similar script. The user nearly executed the command at 4 a.m. but recognised the danger and formatted their computer instead. The account highlights how timing, fatigue, and familiar verification screens can influence decisions when users encounter suspicious instructions.
Crypto investor Alex Clive urged crypto traders to avoid running commands presented through fake verification pages, emphasising that genuine Cloudflare checks operate within the browser. He recommended verifying projects through official X accounts, CoinMarketCap, CoinGecko, or trusted exchange listings, while checking website domains letter by letter. His warning was direct: taking 30 seconds to verify a link can prevent significant financial losses.
Proving you are human, fake VC firms and compromised Chrome extensions keep pushing these click-fix attacks
Cybercriminals are increasingly using fake venture capital firms to target crypto founders and professionals on LinkedIn. According to Moonlock Lab, scammers impersonating firms including SolidBit, MegaBit, and Lumax Capital approach victims with partnership offers before directing them to counterfeit Zoom or Google Meet meeting pages. These websites use fake Cloudflare verification screens to initiate the ClickFix attack.
The campaign relies on social engineering, and victims are instructed to paste a malicious command into their system terminal after clicking a fake verification box, unknowingly executing malware themselves. Moonlock Lab also identified an individual using the alias Mykhailo Hureiev, allegedly presented as SolidBit Capital’s co-founder, as a recurring contact in the outreach campaign.
In a separate campaign, hackers compromised QuickLens, a Chrome extension previously used for Google Lens searches. Annex Security founder John Tuckner reported that ownership changed on February 1, followed by a malicious update that affected approximately 7,000 users. The compromised extension deployed ClickFix scripts and data-stealing tools targeting crypto wallet information, seed phrases, Gmail accounts, login credentials, and payment details.
Enjoyed this? Bookmark DeFi Planet, explore related topics, and follow us on Twitter, LinkedIn, Facebook, Instagram, Threads, and CoinMarketCap Community for seamless access to high-quality industry insights
Take control of your crypto portfolio with DEFI PLANET PRO, DeFi Planet’s suite of analytics tools.